Is there an already registered domain name or an expired one, to which you would like to schedule a reminder for when it becomes available again?
Author: Nabil
[Shared Hosting] How to install redmine on cPanel
As requested by a friend, this is a short video I made to show how to install Redmine on cPanel, this goes for most of the standard Ruby-on-Rails apps.
Reset perfexcrm password from phpMyAdmin
Tested on version 2.9
- Go to phpmyadmin
- Select the database you use for perfex crm
- Select table tblstaff
- Find your account (you can find it by the email field)
- Replace the hash, by pasting into the password column the following hash :
$2a$08$gzXZ8gbnRcKPQOIRi2GnVuy.xXibU1A3msw.wXk.pB6A2wPU29iO2
cPanel NodeJs | ERR_REQUIRE_ESM
If you are using cPanel > Setup Node.Js App and you have across of a similar error to:
Error [ERR_REQUIRE_ESM]: Must use import to load ES Module: app.jsArabicthon #1
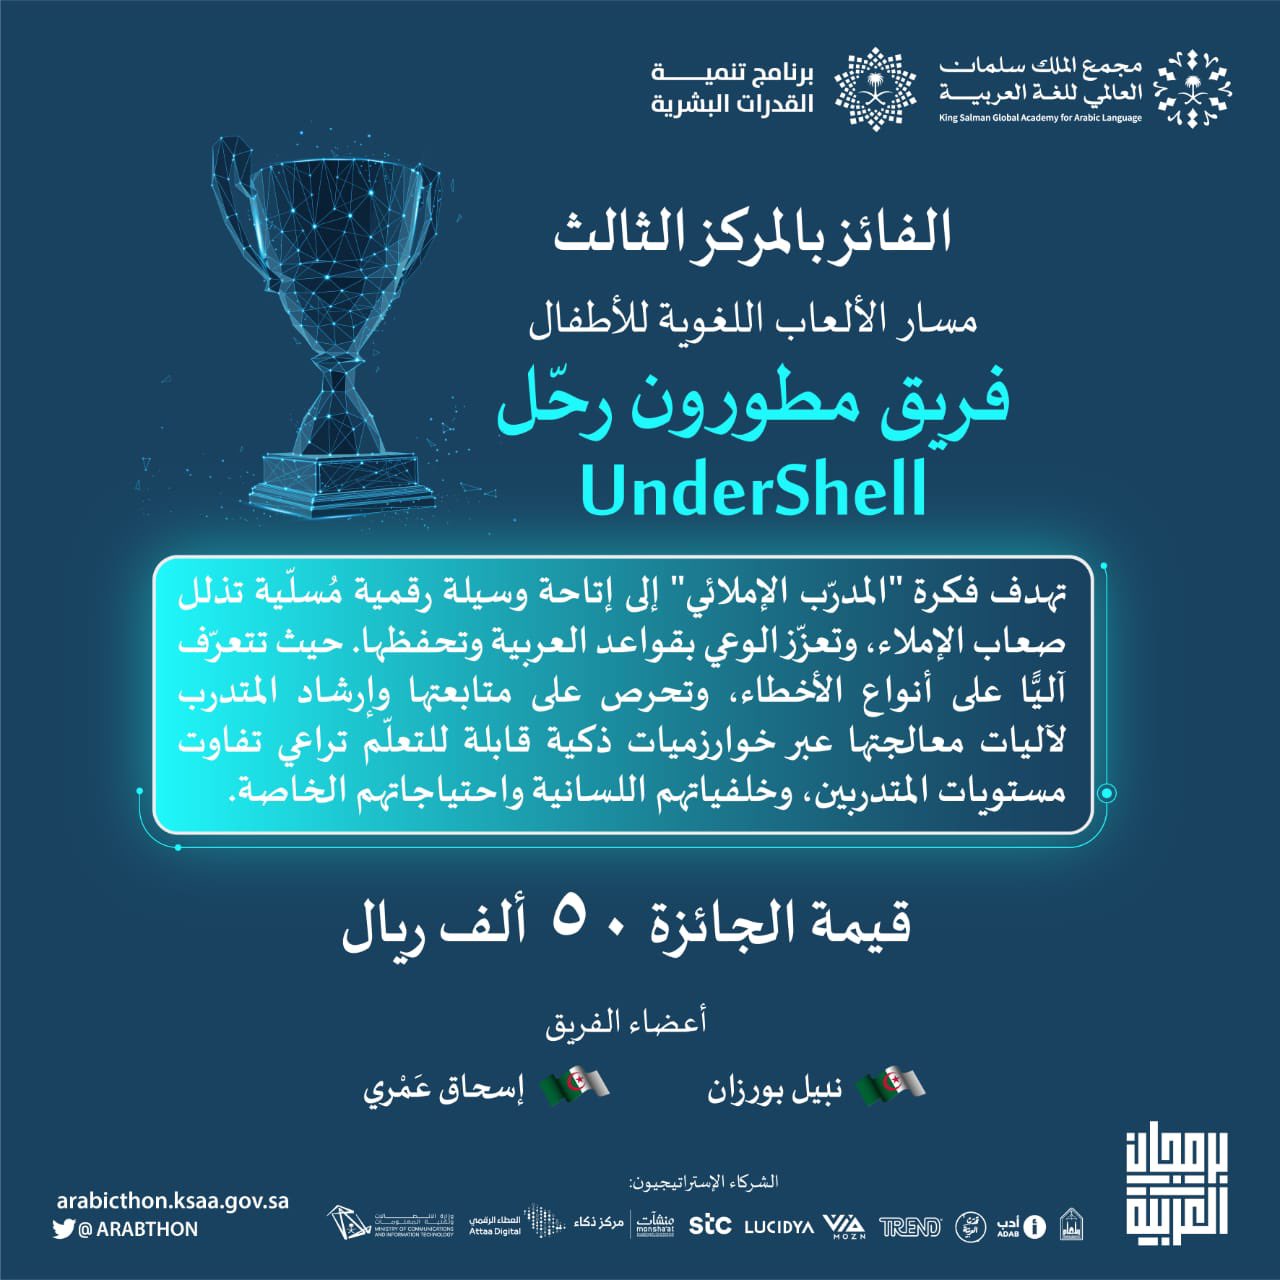
مع كوننا في عصر الرقمنة، فإننا نشهد غياب نماذج رقمية متاحة على مختلف المنصات ولمختلف الفئات للتدرب على الإملاء العربي وتجاوز الأخطاء الشائعة عند الكتابة. وهو مشكل لا يختص بالصغار وإنما يتعدى للكبار خاصة مع انتشار الأخطاء الإملائية عبر وسائل التواصل النصية الحديثة. وإلى جانب ذلك فإن متعلمي العربية من غير الناطقين بها وأصحاب الهمم والبصيرة من المكفوفين مستخدمي قارئ الشاشة، لا يجدون وسائل كافية للتدرب وتحسين إملائهم.
يضاف إلى ذلك: قلة إقبال أو استصعاب شريحة كبيرة من مستخدمي ومتعلمي العربية الرجوع إلى المراجع اللغوية الضابطة للإملاء واستثقالهم للتعليم المباشر لقواعد الإملاء.
Centova & CSF/LFD Firewall
Centova can be installed with cPanel/WHM. but if you are using CSF, you will have to add the needed ports:
https://centova.com/en/faq/cast3/information/configuring_a_firewall_for_centova_cast
However, This is not enough. Centova error:
Unable to access account for username: Cluster host connection failure for Local server: Connection refused (111)
because LFD may block Centova daemons. If you are using WHM, check ConfigServer Security & Firewall > Watch system logs of lfd (/var/log/lfd.log).
[Linux] Remove all empty files (e.g. 0 kb size PHP files)
Amongst the PHP malwares targeting WP plugins’ vulnerabilities I encounter, some generate hundred of thousand of empty files with 0KB size in all folders and sub-folders recursively . which create diversion and affects the inodes capacity of an account. But diversion may not the only goal. as they are generated through an obfuscated code, so I can imagine that these filenames may be part of an obfuscation process. Instead of writing the directives directly in a PHP or text file, the information is gathered through the listing and ordering of the filenames, possible no? Or maybe I’m over-complicating it.
Continue reading
Securing SSH access with Fail2ban and GeoIP filtering
Any service that is exposed to the network is a potential target, and SSH being so widely deployed across the internet means that it represents a very predictable attack surface or attack vector through which people can try to gain access.
If you review the logs for your SSH service running on any widely trafficked server, you will often see repeated, systematic login attempts that represent brute force attacks by users and bots alike.
tail /var/log/auth.logAdvanced SSH Security: Protecting Root Access with Extra Layers
When securing a Linux server, simply using SSH keys and disabling passwords isn’t always enough—especially for root access, which is a prime target for attackers. Restricting IPs or VPN is a good approach but not always possible. To enhance protection, you can implement Port Knocking, ProxyJump/Bastion Host, and Google Authenticator 2FA—but exclusively for root users, while allowing normal users to log in more conveniently.
1. Port Knocking for Root Access
Port Knocking keeps SSH invisible unless a specific sequence of connection attempts is made first. This ensures that only authorized users can expose the SSH port.
- Configure knockd to require knocking only for root login while normal users access SSH normally.
- Example sequence to open SSH:
sequence = 7000,8000,9000 command = iptables -A INPUT -p tcp --dport 22 -s %IP% -j ACCEPT - Restrict SSH for root in
sshd_config:Match User root Port 2222
Now, root users must “knock” to gain access, while normal users use standard SSH.
2. Google Authenticator 2FA for Root
Enforcing multi-factor authentication (MFA) for root ensures extra protection beyond SSH keys.
- Install Google Authenticator:
apt install libpam-google-authenticator
dnf install google-authenticato - Require 2FA only for root in PAM:
Match User root auth required pam_google_authenticator.so - Enforce multiple authentication methods:
Match User root
AuthenticationMethods publickey,password publickey,keyboard-interactive
This setup ensures root users need an extra authentication step, while normal users continue with SSH keys.
If 2FA providers are unavailable, emergency bypass OTP backup codes or physical security tokens can restore access.
3. Bastion Host for Root
A Bastion Host (Jump Host) acts as an intermediary, ensuring direct SSH access to root is not possible.
- Restrict root login to only be allowed from the bastion:
Match User root AllowTcpForwarding no AllowUsers root@bastion-ip - On the client side, enforce ProxyJump:
Host myserver
    User root
    ProxyJump bastion_host
With this setup, attackers cannot SSH directly to the server as root.
Pros & Cons
A Bastion Host is a great security solution, but it comes with both benefits and drawbacks. Here’s a balanced look at its pros and cons.
Pros of Using a Bastion Host
✅ Enhanced Security Layer – It prevents direct SSH access to critical servers, reducing the risk of brute-force attacks.
✅ Centralized Access Control – Acts as a single entry point, making user authentication and permissions easier to manage.
✅ Logging & Auditing – Bastion hosts can record SSH sessions, helping with security monitoring and compliance.
✅ Reduced Attack Surface – Since users must go through the bastion, fewer ports are exposed on the actual servers.
✅ Multi-Factor Authentication (MFA) Support – You can enforce 2FA or biometric authentication for extra security.
Cons of Using a Bastion Host
❌ Single Point of Failure – If the bastion goes down, users may lose access to the entire infrastructure unless backup access is in place.
❌ Performance Bottleneck – If not scaled properly, it can slow down connections, especially with large numbers of users.
❌ Additional Complexity – Requires extra configuration and maintenance, including access rules and monitoring.
❌ Target for Attackers – Since all SSH traffic goes through it, attackers may try to compromise the bastion itself.
Final Thoughts
Verdict: A Bastion Host is an excellent security tool, but it must be hardened properly, monitored, and paired with backups to ensure reliability. E.g.:
iptables -A INPUT -p tcp –dport 22 -s BACKUP_IP -j ACCEPT
Final Thoughts
By combining Port Knocking, Bastion Host restrictions, and 2FA, you can make SSH access to root far more secure while ensuring redundancy in case of root access failure and allowing normal users to log in more conveniently. These techniques significantly reduce the risk of unauthorized access while maintaining a balance between security and usability.
GLIBC & Installing DirectAdmin on Ubuntu 18.04
If you have tried to install DirectAdmin on Ubuntu and received an error related to GNU C Library such as:
/usr/local/directadmin/directadmin: /lib/x86_64-linux-gnu/libc.so.6: version `GLIBC_2.28' not found (required by /usr/local/directadmin/directadmin)
This implies that you have chosen the wrong OS on the ordered license. Ubuntu isn’t yet specifically supported therefore choosing Ubuntu or Debian on the drop-list may not be helpful. Configure rather your license for Linux 64bits.
P.S.: If you encounter a different issue, search directly on DirectAdmin Forums, don’t rely on global search engines.